Security and trust
Support data stays yours. Customers only see what you approve.
Arcus works with tickets, logs and calls. This page explains what we protect, how, and what is not done yet.
How we protect your data
Data isolation per org
Every API request is checked against your org membership. Resolution memory, insights and history never mix between orgs. Cross-org déjà vu matches are off unless you opt in, and even then they are capped at medium confidence.
Encryption
All traffic uses HTTPS. Desktop connector tokens are kept in the operating system keychain, not in plain storage. Org OAuth client secrets are encrypted at rest and never stored in plaintext after save.
Approval before anything public
Arcus writes internal notes on its own. Anything a customer or another team will see (a public reply, a Jira bug, a Slack post) waits for your approval. Auto public replies are off by default and never run on urgent or critical tickets.
Leak guard
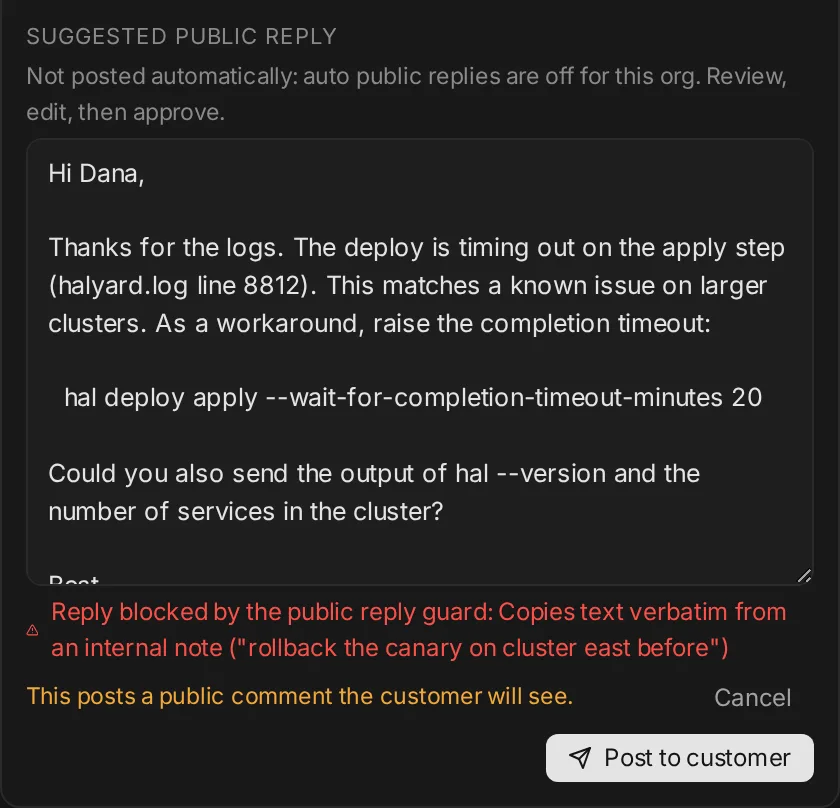
Before a public reply can be posted, it is compared with the ticket’s internal comments. Verbatim internal text, internal-only fixes and internal links block the post and show the reason.
Audit log
Actions are written to a structured audit log with personal data scrubbed. Each first-response run records whether it posted, skipped or failed, its confidence and the public decision.
Least privilege connectors
Zendesk, ServiceNow, Jira and Slack use the token or app your team creates, with the scopes you grant. Disconnect any time in Settings.
The guard in the product
A suggested reply that copied text from an internal note. Posting is blocked until it is fixed.
Status at a glance
| Control | Status | Details |
|---|---|---|
| Per-org data isolation | In place | API routes check org membership on every request. Déjà vu, insights and call history are scoped to your org. |
| Encryption in transit | In place | HTTPS only, with TLS terminated at the host and HSTS set. |
| Credential storage | In place | Desktop connector tokens live in the OS keychain (Electron safeStorage). Org OAuth client secrets are encrypted at rest (Fernet). |
| Approval before public posts | In place | Public replies, Jira bugs and Slack posts need an explicit approval. Auto public replies are off by default. |
| Public reply guard | In place | Drafts are checked against internal comments before they can be posted. |
| Audit log | In place | Structured audit events with PII scrubbing, including every first-response run and its public decision. Org admins can filter and export it as CSV. |
| Sign-in | Google, GitHub, email, SSO | OAuth sign-in with Google or GitHub, email, or your company SSO. |
| SAML / enterprise SSO | In place | SAML 2.0 and OpenID Connect SSO with SCIM 2.0 user provisioning, tested against Okta and Microsoft Entra ID (Azure AD). Admins can require SSO for their domain. |
| SOC 2 | Not certified | We hold no certifications today. SOC 2 is planned but not started; we will not claim otherwise. |
What leaves your machine
- Live call audio is streamed to the Arcus API and transcribed while the call runs.
- Ask sends only the context you include: ticket, notes, transcript and code snippets.
- Your local code index stays on your computer. Snippets are sent only when you ask about them.
- Screen stills stay on your computer until you send them.
See the subprocessors list and the privacy policy. Report a vulnerability to daarishlomo@gmail.com.